

2023 Updated Verified MS-500 Downloadable Printable Exam Dumps
The Ultimate Microsoft MS-500 Dumps PDF Review
The MS-500 exam is intended for security administrators and professionals who work with Microsoft 365 technologies. To be eligible for this exam, candidates must have a solid understanding of Microsoft 365 security technologies and experience in deploying, managing, and monitoring security solutions for Microsoft 365. This certification exam is ideal for those who are keen on expanding their knowledge and skills in Microsoft 365 security administration and want to advance their careers.
NEW QUESTION # 166
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: #HSP.ug?$p6un
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11122308



You need to ensure that a user named Allan Deyoung receives incident reports when email messages that contain data covered by the U.K. Data Protection Act are sent outside of your organization.
To complete this task, sign in to the Microsoft 365 admin center.
Answer:
Explanation:
1. In the Security & Compliance Center > left navigation > Data loss prevention > Policy > + Create a policy.
2. Choose the U.K. Data Protection Act template > Next.
3. Name the policy > Next.
4. Choose All locations in Office 365 > Next.
5. At the first Policy Settings step just accept the defaults,
6. After clicking Next, you'll be presented with an additional Policy Settings page Deselect the Show policy tips to users and send them an email notification option.
Select the Detect when content that's being shared contains option, and configure the number instances to be 10.
Select the Send incident reports in email option.
Select the Choose what to include in the report and who receives it link to add Allan Deyoung as a recipient.
7. > Next
8. Select the option to turn on the policy right away > Next.
9. Click Create to finish creating the policy.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-test-tune-dlp-policy?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/compliance/data-loss-prevention-policies?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/compliance/what-the-dlp-policy-templates-include?view=o365-worldwide
NEW QUESTION # 167
You have a Microsoft 365 subscription that uses a default domain name of contoso.com.
Microsoft Azure Active Directory (Azure AD) contains the users shown in the following table.
Microsoft Intune has two devices enrolled as shown in the following table:
Both devices have three apps named App1, App2, and App3 installed.
You create an app protection policy named ProtectionPolicy1 that has the following settings:
Protected apps: App1
Exempt apps: App2
Windows Information Protection mode: Block
You apply ProtectionPolicy1 to Group1 and Group3. You exclude Group2 from ProtectionPolicy1.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.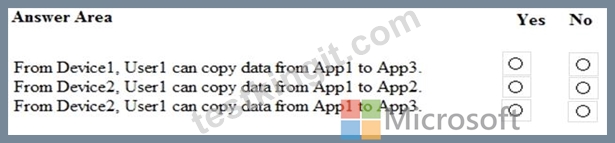
Answer:
Explanation:
NEW QUESTION # 168
You have a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.
You create and enforce an Azure AD Identity Protection sign-in risk policy that has the following settings:
* Assignments: Include Group1, Exclude Group2
* Conditions: Sign in risk of Low and above
* Access: Allow access, Require password multi-factor authentication
You need to identify how the policy affects User1 and User2.
What occurs when each user signs in from an anonymous IP address? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation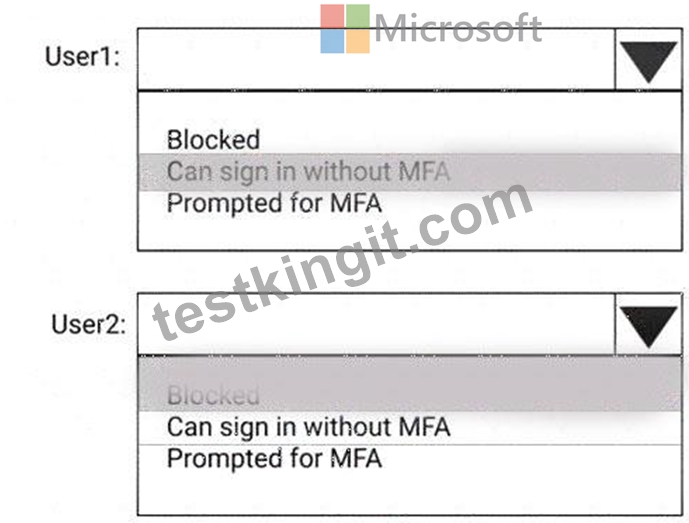
NEW QUESTION # 169
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: &=Q8v@2qGzYz
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11032396
You need to ensure that a user named Lee Gu can manage all the settings for Exchange Online. The solution must use the principle of least privilege.
To complete this task, sign in to the Microsoft Office 365 admin center.
Answer:
Explanation:
See explanation below.
* In the Exchange Administration Center (EAC), navigate to Permissions > Admin Roles.
* Select the group: Organization Management and then click on Edit.
* In the Members section, click on Add.
* Select the users, USGs, or other role groups you want to add to the role group, click on Add, and then click on OK.
* Click on Save to save the changes to the role group.
Reference:
https://help.bittitan.com/hc/en-us/articles/115008104507-How-do-I-assign-the-elevated-admin-role-Organization
https://docs.microsoft.com/en-us/exchange/permissions-exo/permissions-exo
NEW QUESTION # 170
You have a Microsoft 365 subscription that uses a default name of litwareinc.com.
You configure the Sharing settings in Microsoft OneDrive as shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.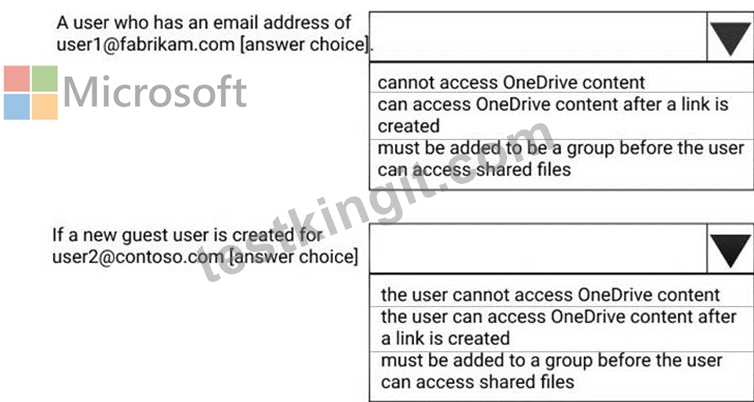
Answer:
Explanation: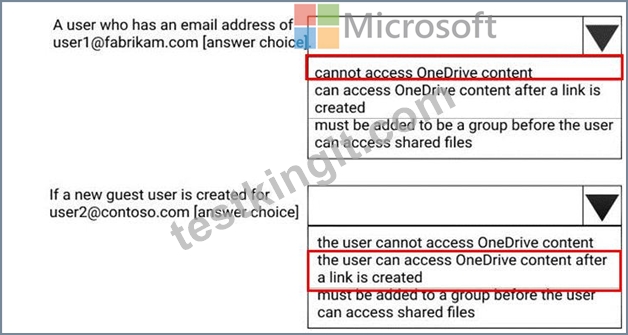
References:
https://docs.microsoft.com/en-us/onedrive/manage-sharing
NEW QUESTION # 171
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Identity.
You receive the following alerts:
* Suspected Netlogon privilege elevation attempt
* Suspected Kerberos SPN exposure
* Suspected DCSync attack
To which stage of the cyber-attack kill chain does each alert map? To answer, drag the appropriate alerts to the correct stages. Each alert may be used once. more than once, or rot at all. You may need to drag the split bar between panes or scroll to view content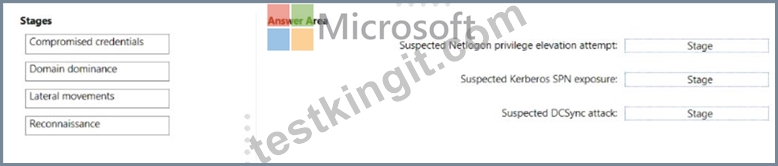
Answer:
Explanation: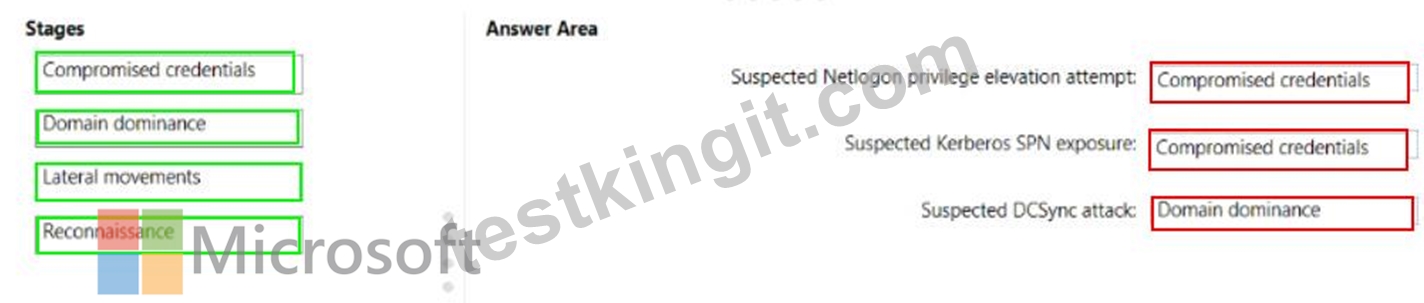
NEW QUESTION # 172
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: #HSP.ug?$p6un
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11122308




You need to ensure that a user named Allan Deyoung uses multi-factor authentication (MFA) for all authentication requests.
To complete this task, sign in to the Microsoft 365 admin center.
Answer:
Explanation:
1. Open the Admin Center and go to Users > Active Users
2. Open Multi-factor authentication
Don't select any user yet, just open the Multi-factor authentication screen. You will find the button in the toolbar.
3. Open the Service settings
Before we start enabling MFA for the users, we first go through the service settings. The button to the settings screen doesn't stand out, but it's just below the title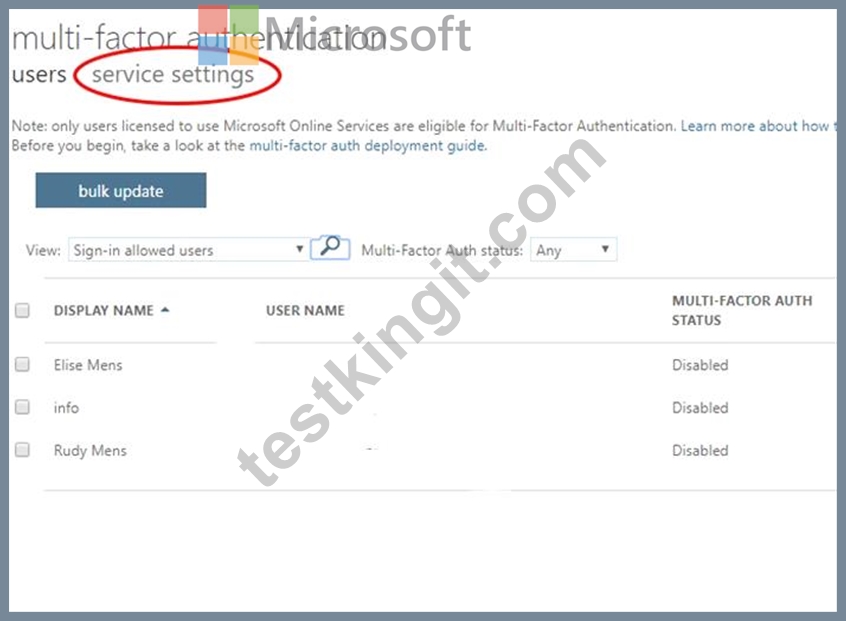
4. Setup MFA Office 365
A few settings are important here:
Make sure you check the App password. Otherwise, users can't authenticate in some applications (like the default mail app in Android).
Also, take a look at the remember function. By default, it is set to 14 days.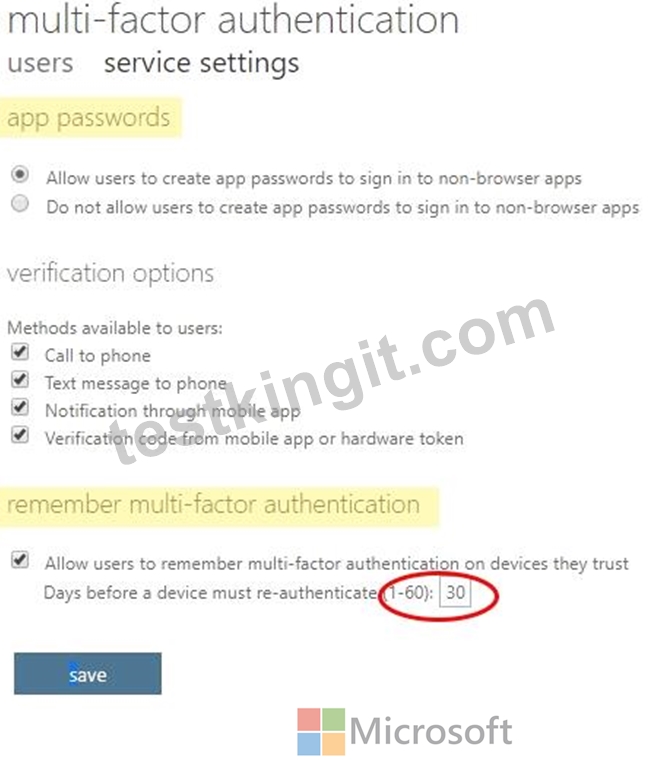
5. Enable MFA for Office 365 users
After you have set the settings to your liking click on save and then on users (just below the title Multi-factor authentication).
You see the list of your users again. Here you can select single or multiple users to enable MFA.
At the moment you enable Office 365 MFA for a user it can get the setup screen as soon as the users browse to one of the Office 365 products.
Reference:
https://lazyadmin.nl/office-365/how-to-setup-mfa-in-office-365/
NEW QUESTION # 173
You configure Microsoft Azure Active Directory (Azure AD) Connect as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: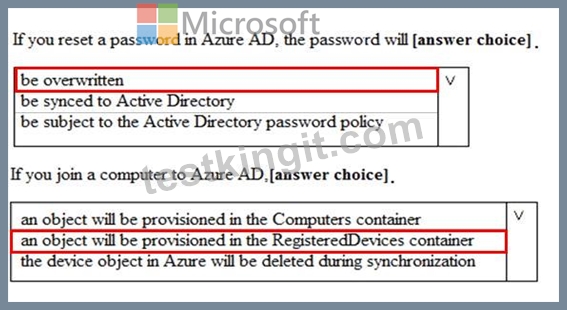
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-device-writeback
NEW QUESTION # 174
You have an Azure Sentinel workspace.
You configure a rule to generate Azure Sentinel alerts when Azure Active Directory (Azure AD) Identity Protection detects risky sign-ins. You develop an Azure Logic Apps solution to contact users and verify whether reported risky sign-ins are legitimate.
You need to configure the workspace to meet the following requirements:
Call the Azure logic app when an alert is triggered for a risky sign-in.
To the Azure Sentinel portal, add a custom dashboard that displays statistics for risky sign-ins that are detected and resolved.
What should you configure in Azure Sentinel to meet each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.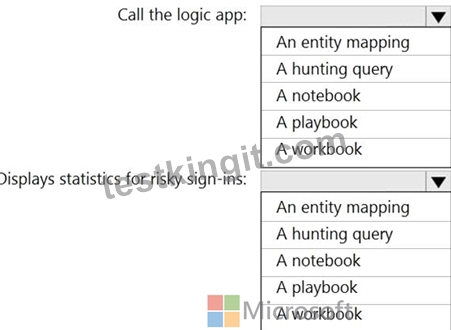
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-respond-threats-playbook
NEW QUESTION # 175
Which users are members of ADGroup1 and ADGroup2? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: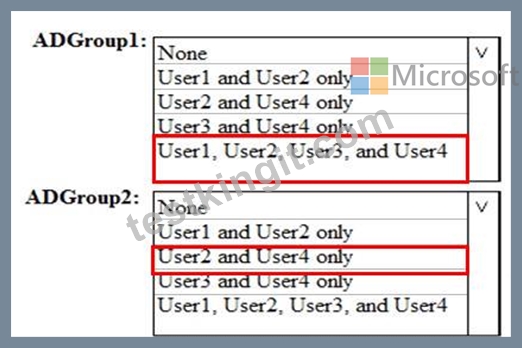
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/users-groups-roles/groups-dynamic-membership#supported-values
NEW QUESTION # 176
You need to create a policy that identifies content in Microsoft OneDrive that contains credit card numbers.
To complete this task, sign in to the Microsoft 365 portal.
Answer:
Explanation:
See explanation below.
Explanation
You need to configure auto-labeling in 'simulation' mode. In the policy, you can select the 'Credit Card' sensitive info type.
* In the Microsoft 365 compliance center, navigate to sensitivity labels:
Solutions > Information protection
* Select the Auto-labeling (preview) tab.
* Select + Create policy.
* For the page Choose info you want this label applied to: Select one of the templates, such as Financial or Privacy. You can refine your search by using the Show options for dropdown. Or, select Custom policy if the templates don't meet your requirements. Select Next.
* For the page Name your auto-labeling policy: Provide a unique name, and optionally a description to help identify the automatically applied label, locations, and conditions that identify the content to label.
* For the page Choose locations where you want to apply the label: Select OneDrive. Then select Next.
* For the Define policy settings page: Keep the default of Find content that contains to define rules that identify content to label across all your selected locations. The rules use conditions that include sensitive information types and sharing options. For sensitive information types, you can select both built-in and custom sensitive information types.
* Then select Next.
* For the Set up rules to define what content is labeled page: Select + Create rule and then select Next.
* On the Create rule page, name and define your rule, using sensitive information types and then select Save.
* Click Next.
* For the Choose a label to auto-apply page: Select + Choose a label, select a label from the Choose a sensitivity label pane, and then select Next.
* For the Decide if you want to run policy simulation now or later page: Select Run policy in simulation mode if you're ready to run the auto-labeling policy now, in simulation mode. Otherwise, select Leave policy turned off. Select Next.
* For the Summary page: Review the configuration of your auto-labeling policy and make any changes that needed, and complete the wizard.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365-wo
NEW QUESTION # 177
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some questions sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription.
You have a user named User1. Several users have full access to the mailbox of User1.
Some email messages sent to User1 appear to have been read and deleted before the user viewed them.
When you search the audit log in Security & Compliance to identify who signed in to the mailbox of User1, the results are blank.
You need to ensure that you can view future sign-ins to the mailbox of User1.
You run the Set-MailboxFolderPermission -Identity "User1"
-User [email protected] -AccessRights Owner command.
Does that meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Explanation/Reference:
References:
https://docs.microsoft.com/en-us/powershell/module/exchange/mailboxes/set-mailbox?view=exchange-ps
NEW QUESTION # 178
Your network contains an on-premises Active Directory domain named contoso.com. The domain contains the groups shown in the following table.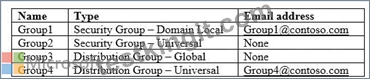
The domain is synced to a Microsoft Azure Active Directory (Azure AD) tenant that contains the groups shown in the following table.
You create an Azure Information Protection policy named Policy1.
You need to apply Policy1.
To which groups can you apply Policy1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: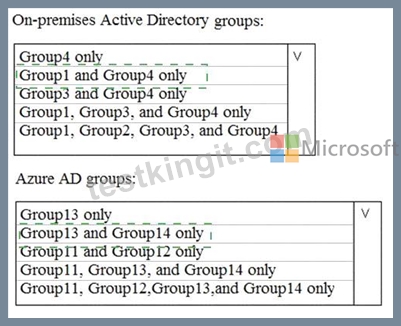
Explanation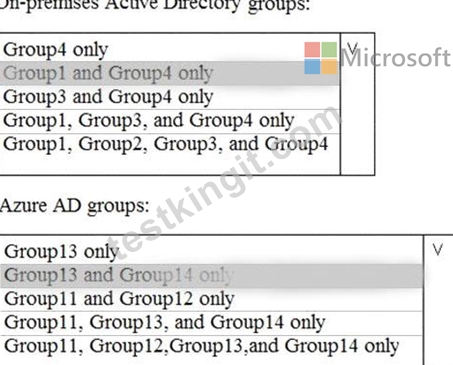
Reference:
https://docs.microsoft.com/en-us/azure/information-protection/prepare
NEW QUESTION # 179
You install Azure ATP sensors on domain controllers.
You add a member to the Domain Admins group. You view the timeline in Azure ATP and discover that information regarding the membership change is missing.
You need to meet the security requirements for Azure ATP reporting.
What should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure-advanced-threat-protection/atp-advanced-audit-policy
NEW QUESTION # 180
You have a hybrid Microsoft Exchange Server organization. All users have Microsoft 365 E5 licenses. You plan to implement an Advanced Threat Protection (ATP) anti-phishing policy. You need to enable mailbox intelligence for all users. What should you do first?
- A. Configure attribute filtering in Microsoft Azure Active Directory Connect (Azure AD Connect).
- B. Purchase the ATP add-on.
- C. Migrate the on-premises mailboxes to Exchange Online.
- D. Select Directory extension attribute sync in Microsoft Azure Active Directory Connect {Azure AD Connect).
Answer: C
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/set-up-anti-phishing-policies
NEW QUESTION # 181
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
You have the devices shown in the following table.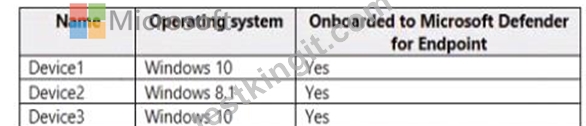
You have the Microsoft Defender for Endpoint portal roles shown in the following table.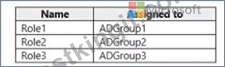
You have the Microsoft Defender for Endpoint device groups shown in the following table.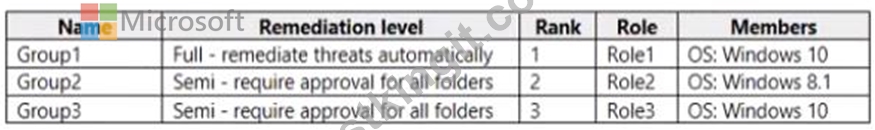
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.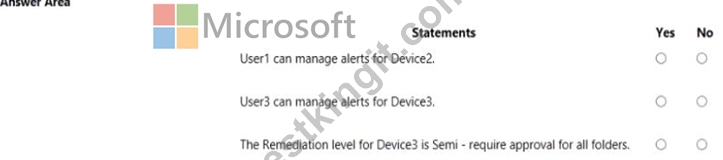
Answer:
Explanation:
NEW QUESTION # 182
You have a Microsoft 365 subscription. From the Security & Compliance admin center, you create the retention policies shown in the following table.
Policy1 if configured as showing in the following exhibit.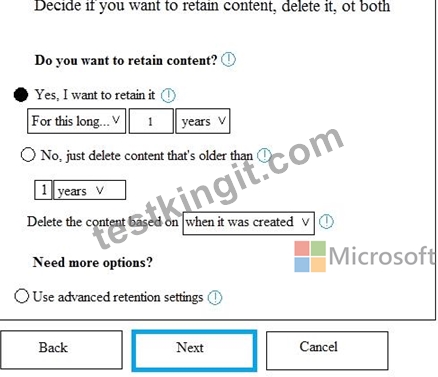
Policy2 is configured as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.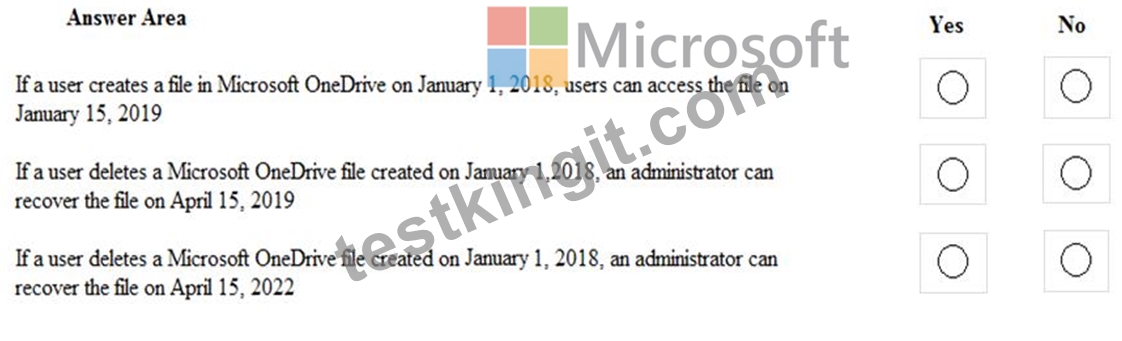
Answer:
Explanation: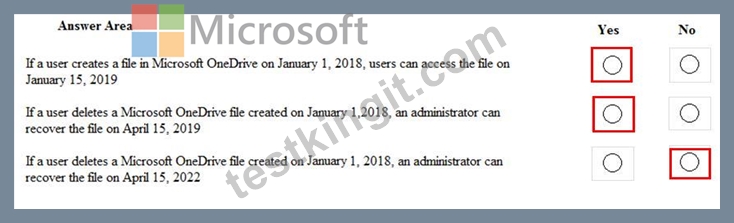
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/retention-policies?redirectSourcePath=%252fen-us%252farticle%252fOverview-of-retention-policies-5e377752-700d-4870-9b6d-12bfc12d2423#the-principles-of-retention-or-what-takes-precedence
NEW QUESTION # 183
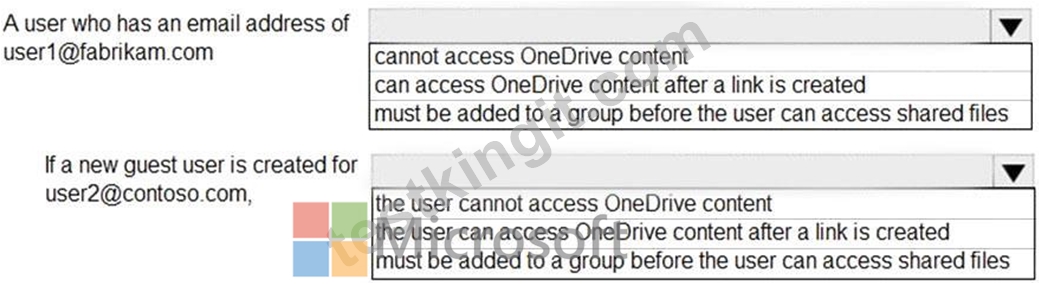
You have a Microsoft 365 subscription that uses a default domain name of litwareinc.com.
You configure the Sharing settings in Microsoft OneDrive as shown in the following exhibit.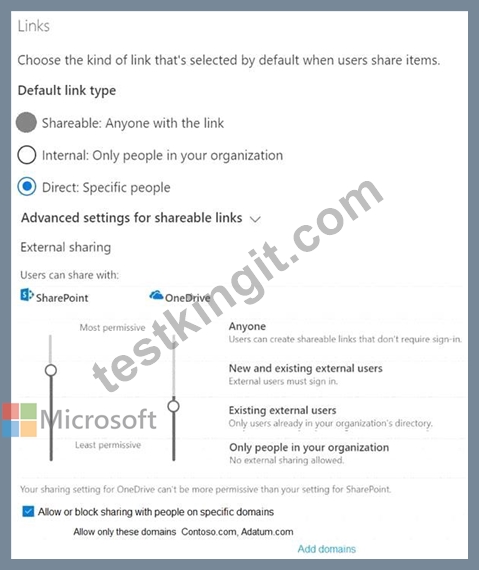
Answer:
Explanation:
Explanation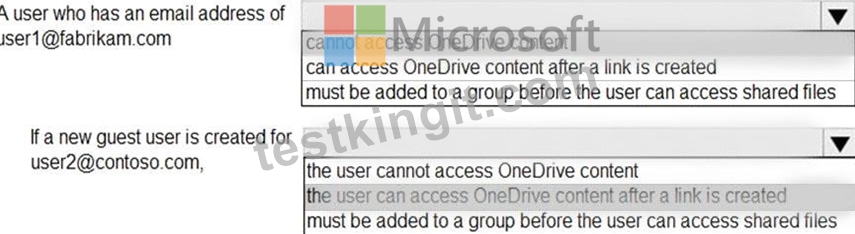
Reference:
https://docs.microsoft.com/en-us/sharepoint/turn-external-sharing-on-or-off
NEW QUESTION # 184
You have a Microsoft 365 subscription. Auditing is enabled.
A user named User1 is a member of a dynamic security group named Group1.
You discover that User1 is no longer a member of Group1.
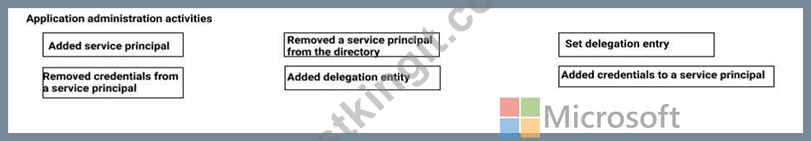
You need to search the audit log to identify why User1 was removed from Group1.
Which two actions should you use in the search? To answer, select the appropriate activities in the answer area.
NOTE: Each correct selection is worth one point.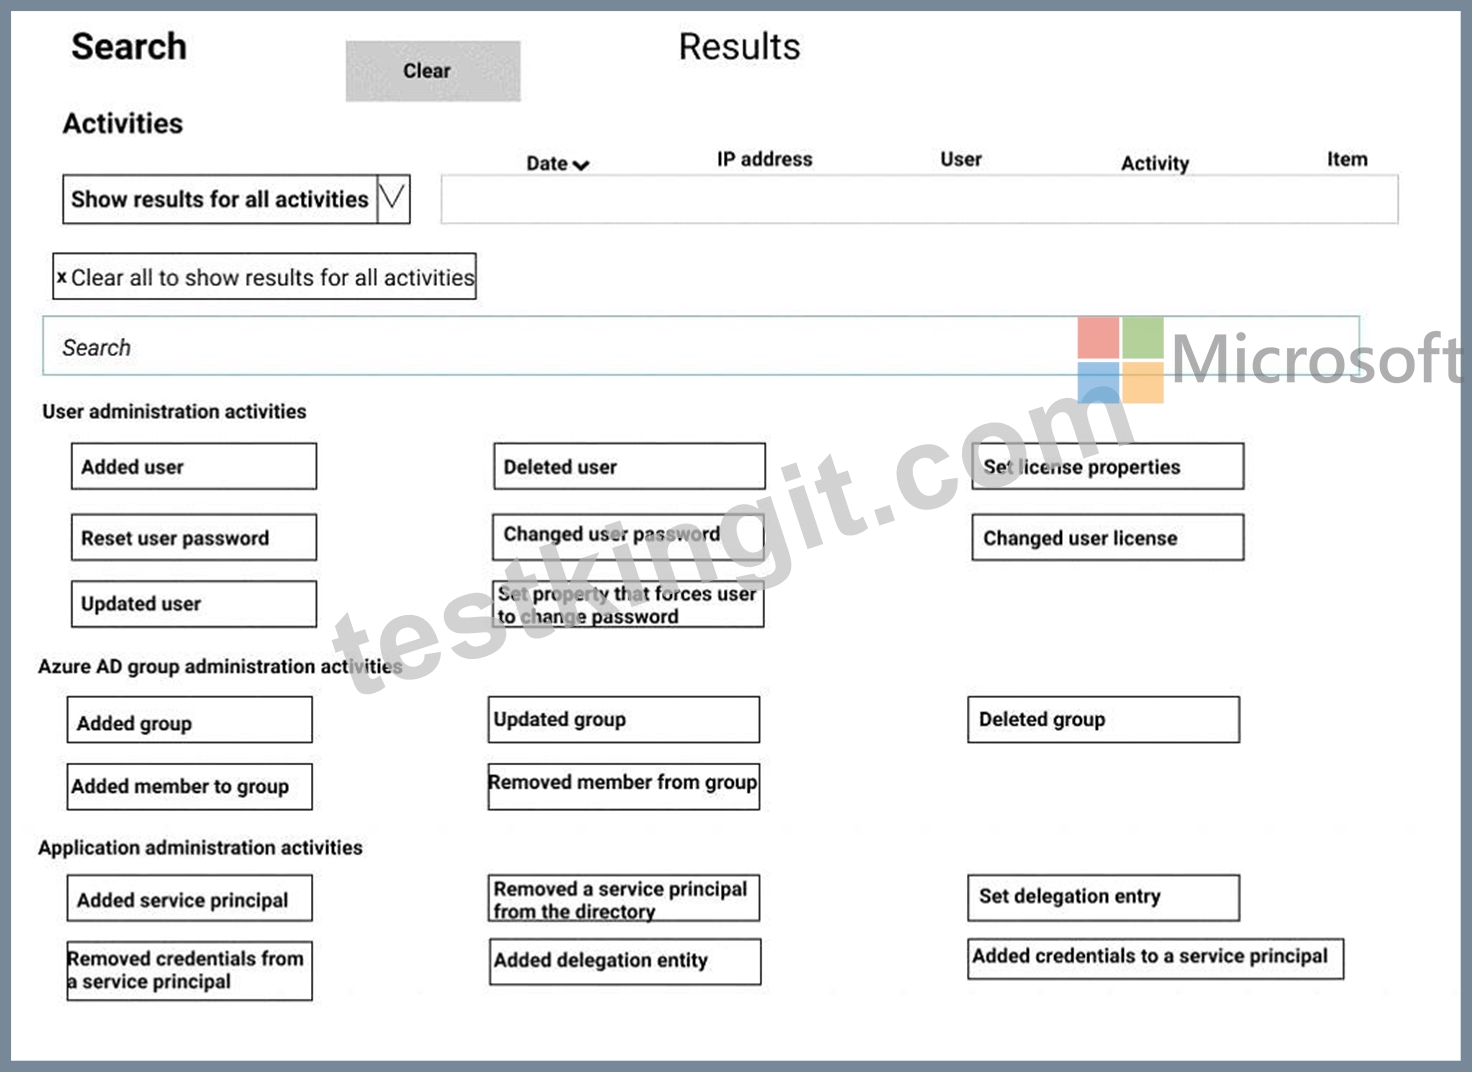
Answer:
Explanation: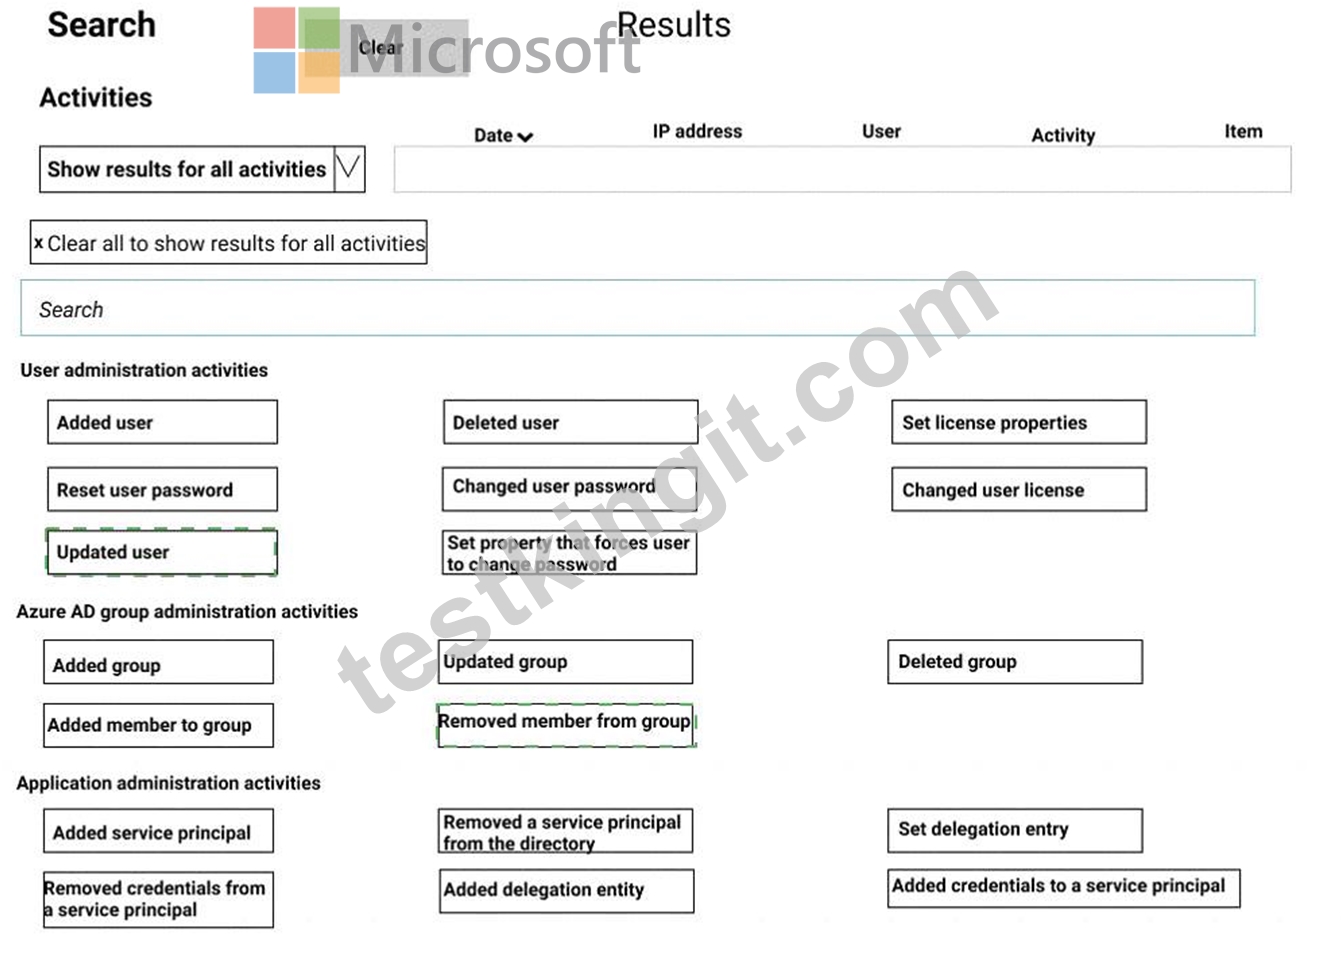
Explanation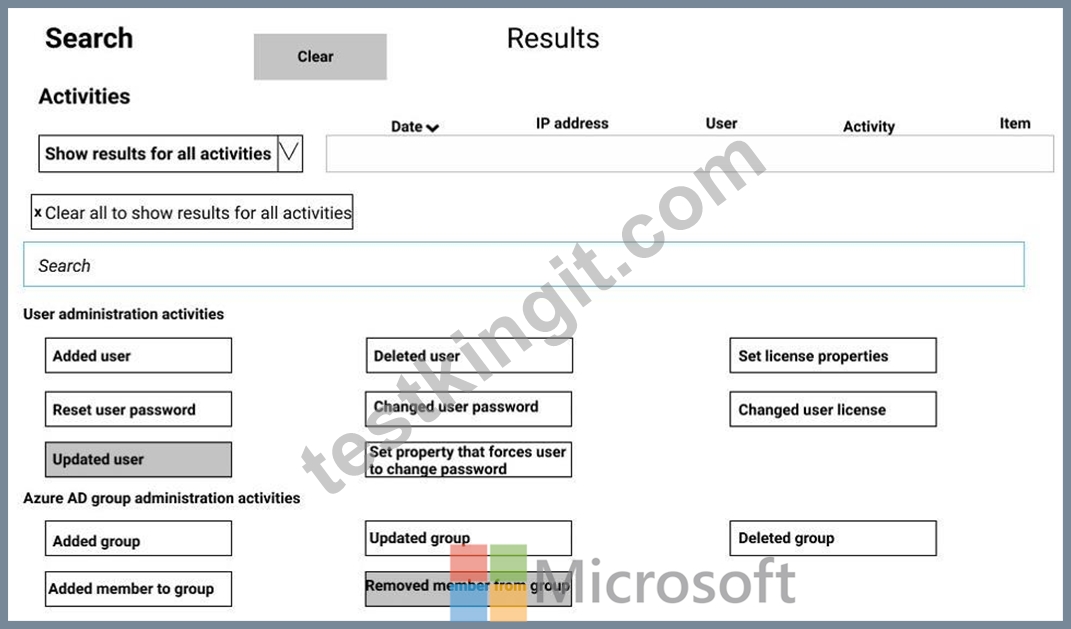
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/search-the-audit-log-in-security-and-compliance
NEW QUESTION # 185
Note: This question is part of series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 E5 subscription that is associated to a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com.
You use Active Directory Federation Services (AD FS) to federate on-premises Active Directory and the tenant. Azure AD Connect has the following settings:
* Source Anchor: objectGUID
* Password Hash Synchronization: Disabled
* Password writeback: Disabled
* Directory extension attribute sync: Disabled
* Azure AD app and attribute filtering: Disabled
* Exchange hybrid deployment: Disabled
* User writeback: Disabled
You need to ensure that you can use leaked credentials detection in Azure AD Identity Protection.
Solution: You modify the Source Anchor settings.
Does that meet the goal?
- A. Yes
- B. No
Answer: B
NEW QUESTION # 186
Which IP address space should you include in the MFA configuration?
- A. 172.16.0.0/24
- B. 192.168.0.0/20
- C. 192.168.16.0/20
- D. 131.107.83.0/28
Answer: C
NEW QUESTION # 187
You have a Microsoft 365 subscription that uses an Azure Active Directory (Azure AD) tenant named contoso.com. All the devices in the tenant are managed by using Microsoft Intune.
You purchase a cloud app named App1 that supports session controls.
You need to ensure that access to App can be reviewed in real time.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation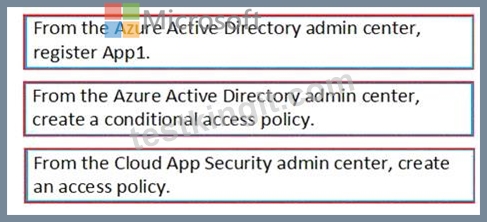
References:
https://docs.microsoft.com/en-us/cloud-app-security/access-policy-aad
NEW QUESTION # 188
Your network contains an on-premises Active Directory domain named contoso.com. The domain contains the groups shown in the following table.
The domain is synced to a Microsoft Azure Active Directory (Azure AD) tenant that contains the groups shown in the following table.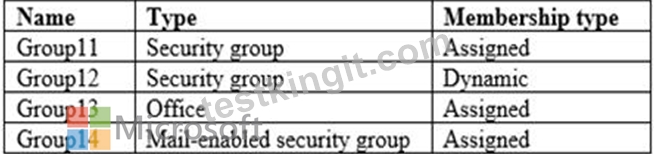
You create an Azure Information Protection policy named Policy1.
You need to apply Policy1.
To which groups can you apply Policy1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.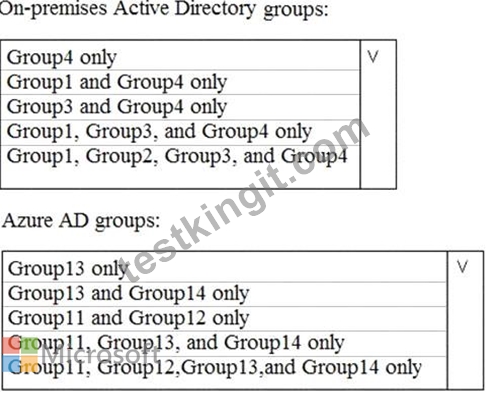
Answer:
Explanation: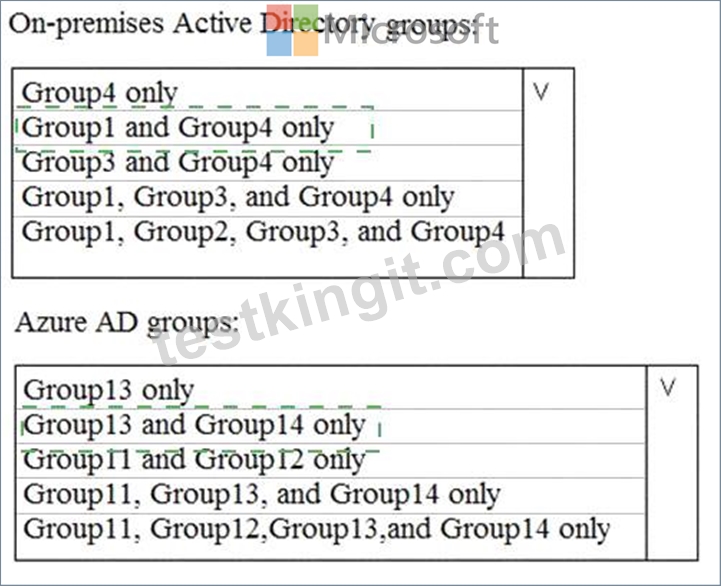
Explanation
Reference:
https://docs.microsoft.com/en-us/azure/information-protection/prepare
NEW QUESTION # 189
You have a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com.
Four Windows 10 devices are joined to the tenant as shown in the following table.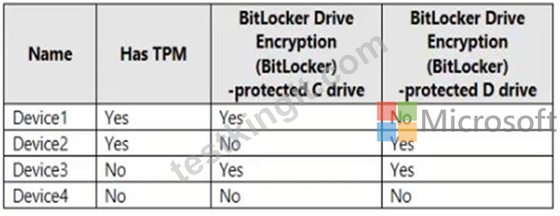
On which devices can you use BitLocker To Go and on which devices can you turn on auto-unlock? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.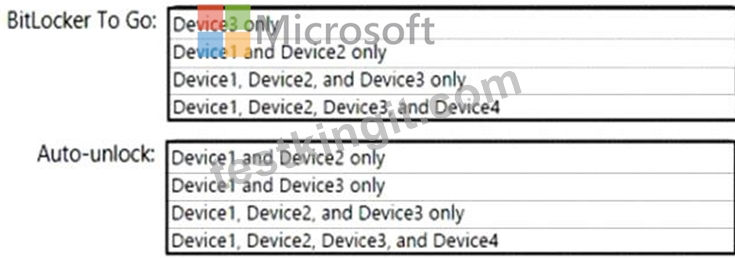
Answer:
Explanation:
Explanation
NEW QUESTION # 190
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription that contains the users shown in the following table.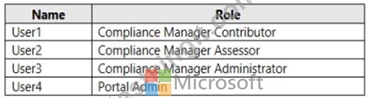
You discover that all the users in the subscription can access Compliance Manager reports.
The Compliance Manager Reader role is not assigned to any users.
You need to recommend a solution to prevent a user named User5 from accessing the Compliance Manager reports.
Solution: You recommend modifying the licenses assigned to User5.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION # 191
......
The Microsoft MS-500 (Microsoft 365 Security Administration) Exam is a highly valuable certification for IT professionals who are responsible for managing and securing Microsoft 365 Enterprise environments. By passing this exam, candidates can demonstrate their proficiency in designing and implementing security policies, managing and monitoring security and compliance solutions, and responding to security incidents.
Achive your Success with Latest MS-500 Exam: https://selftestengine.testkingit.com/Microsoft/latest-MS-500-exam-dumps.html