

MS-500 Exam Dumps - Try Best MS-500 Exam Questions from Training Expert TestKingsIT
Practice Examples and Dumps & Tips for 2022 Latest MS-500 Valid Tests Dumps
The benefits of Obtaining the Microsoft MS-500 Exam Certification:
- The individual will have proof of their knowledge in the computer networking/security areas, which will give them an advantage in the job market. Useable skills of the individual will be very important. Hundreds of job interviews are usually conducted in the IT industry due to the high number of job openings in this field.
- They will be skilled in most areas of computer networking, which will help them increase their income, and give them more job opportunities. Threats posed by hackers, computer viruses, and phishing scams will be no longer a concern for the individual with the MS-500 certification. Harder to crack systems used in manufacturing, banking industries, and business will be under their control.
- The individual who would like to be certified in most areas of computer networking/security would like to be certified by Microsoft or other similar companies, they can show this certification to many employers around the world that are looking for qualified individuals for this specific area.
- They would like to be certified by Microsoft, would like to get a job with the computer networking/security field. Protecting the computer systems of the individual, their employers, and others in their organizations would be their main priority.
- They would like to get a résumé that has their certification, they will show this certification on their resume, which will make employers see them in a different light and give them an advantage when applying for the job. Future job opportunities will be opened to them.
- They would like to help their family members who are looking to work in this field, they can use this certification as one of their qualifications to apply for the job, which will give them an advantage over other candidates that do not have this specific MS-500 Certification or equivalent experience.
Advantages of taking exam dumps of Certification Questions
- Avoid unnecessary stress and get a good score without any distractions.
- Save time and achieve maximum results in a lesser amount of time. This detailed and verified solution will help you to increase the ability of the candidate and be an expert in few days. Tasks and details that should be mastered are provided.
- Study more effectively by focusing on a few questions at a time with an effective study plan.
- Get a better idea of how the exam will be designed, allowing you to prep more effectively for the exam taking itself. Created by our Certified Professionals. Guarantee for existent and valid. Formats are totally the same as the actual exam. Completing the questions and answers assures you acquire the course understanding and details you want.
- Get more confidence from being able to take exams from top-rated organizations using certified paid exam dumps, allowing the candidate to get the most out of their study plan. Implementation of this product will give you peace of mind by allowing you to enjoy a more pleasurable study process. You will love the experience when you will evaluate the incredible solutions of practice exams of this MS-500 Dumps in an efficient way.
- Get the maximum amount of questions answered correctly in the shortest period of time, giving you more time to focus on other aspects of certification.
NEW QUESTION 147
You configure several Advanced Threat Protection (ATP) policies in a Microsoft 365 subscription.
You need to allow a user named User1 to view ATP reports in the Threat management dashboard.
Which role provides User1with the required role permissions?
- A. Message center reader
- B. Information Protection administrator
- C. Security reader
- D. Compliance administrator
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/view-reports-for-atp#what-permissions-areneede
NEW QUESTION 148
Which role should you assign to User1?
- A. Global administrator
- B. Security administrator
- C. User administrator
- D. Privileged role administrator
Answer: B
Explanation:
Explanation
https://docs.microsoft.com/en-us/azure/active-directory/privileged-identity-management/pim-how-to-give-access
NEW QUESTION 149
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription that contains the users shown in the following table.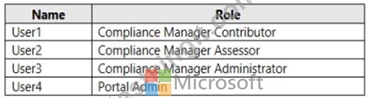
You discover that all the users in the subscription can access Compliance Manager reports.
The Compliance Manager Reader role is not assigned to any users.
You need to recommend a solution to prevent a user named User5 from accessing the Compliance Manager reports.
Solution: You recommend modifying the licenses assigned to User5.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
NEW QUESTION 150
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
You need to identify which user can enable Microsoft Defender Advanced Threat Protection (Microsoft Defender ATP) roles.
Which user should you identify?
- A. User1
- B. User2
- C. User3
- D. User4
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/rbac
NEW QUESTION 151
You need to implement a solution to manage when users select links in documents or email messages from Microsoft Office 365 ProPlus applications or Android devices. The solution must meet the following requirements:
* Block access to a domain named fabrikam.com
* Store information when the users select links to fabrikam.com
To complete this task, sign in to the Microsoft 365 portal.
Answer:
Explanation:
You need to configure a Safe Links policy.
* Go to the Office 365 Security & Compliance admin center.
* Navigate to Threat Management > Policy > Safe Links.
* In the Policies that apply to the entire organization section, select Default, and then click the Edit icon.
* In the Block the following URLs section, type in *.fabrikam.com. This meets the first requirement in the question.
* In the Settings that apply to content except email section, untick the checkbox labelled Do not track when users click safe links. This meets the second requirement in the question.
* Click Save to save the changes.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/office-365-security/set-up-atp-safe-links-policies?view=
NEW QUESTION 152
You have a Microsoft 365 E5 subscription.
From Microsoft Azure Active Directory (Azure AD), you create a security group named Group1. You add 10 users to Group1.
You need to apply app enforced restrictions to the members of Group1 when they connect to Microsoft Exchange Online from non-compliant devices, regardless of their location.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.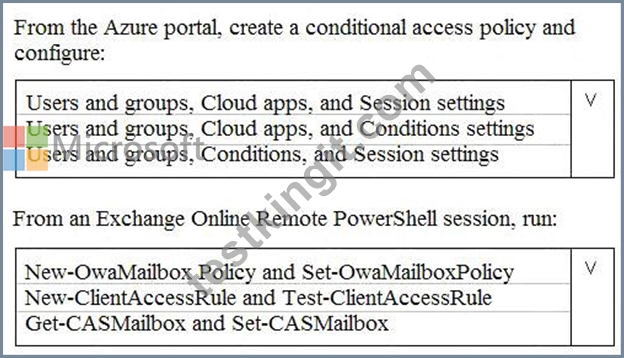
Answer:
Explanation: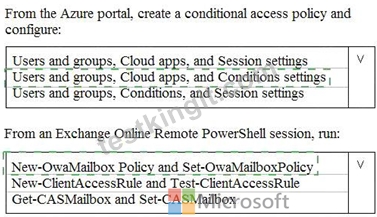
Explanation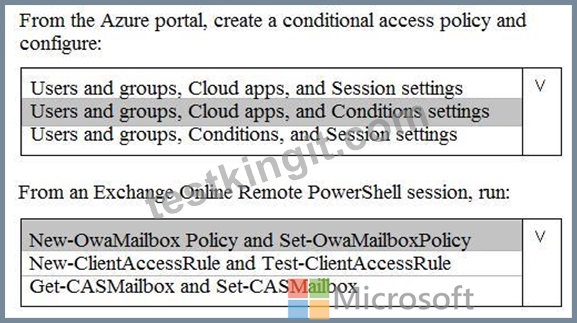
NEW QUESTION 153
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: #HSP.ug?$p6un
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11122308



You need to create an eDiscovery case that places a hold on the mailbox of a user named Allan Deyoung. The hold must retain email messages that have a subject containing the word merger or the word Contoso.
To complete this task, sign in to the Microsoft 365 admin center.
Answer:
Explanation:
1. Navigate to eDiscovery in the Security & Compliance Center, and then click Create a case.
2. On the New Case page, give the case a name, type an optional description, and then click Save. The case name must be unique in your organization.
The new case is displayed in the list of cases on the eDiscovery page. You can hover the cursor over a case name to display information about the case, including the status of the case (Active or Closed), the description of the case (that was created in the previous step), and when the case was changed last and who changed it.
To create a hold for an eDiscovery case:
1. In the Security & Compliance Center, click eDiscovery > eDiscovery to display the list of cases in your organization.
2. Click Open next to the case that you want to create the holds in.
3. On the Home page for the case, click the Hold tab.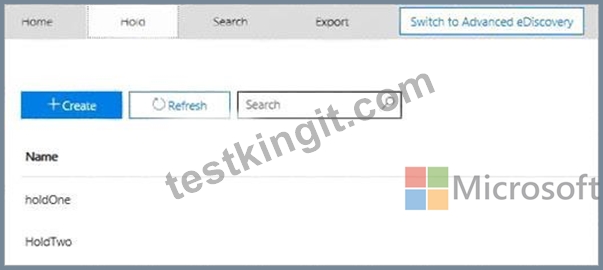
4. On the Hold page, click Create.
5. On the Name your hold page, give the hold a name. The name of the hold must be unique in your organization.
6. (Optional) In the Description box, add a description of the hold.
7. Click Next.
8. Choose the content locations that you want to place on hold. You can place mailboxes, sites, and public folders on hold.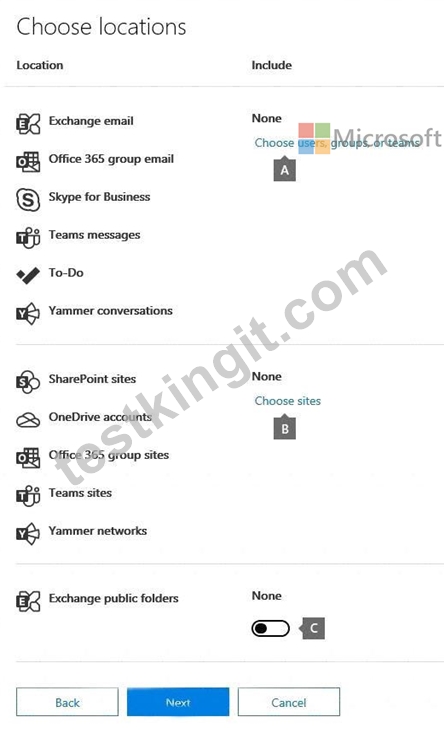
* Exchange email - Click Choose users, groups, or teams and then click Choose users, groups, or teams
* again. to specify mailboxes to place on hold. Use the search box to find user mailboxes and distribution groups (to place a hold on the mailboxes of group members) to place on hold. You can also place a hold on the associated mailbox for a Microsoft Team, a Yammer Group, or an Office 365 Group. Select the user, group, team check box, click Choose, and then click Done.
Note
When you click Choose users, groups, or teams to specify mailboxes to place on hold, the mailbox picker that's displayed is empty. This is by design to enhance performance. To add people to this list, type a name (a minimum of 3 characters) in the search box.
9. After configuring a query-based hold, click Next.
10. Review your settings, and then click Create this hold.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/ediscovery-cases?view=o365-worldwide#step-4-pla
NEW QUESTION 154
Your company has a main office and a Microsoft 365 subscription.
You need to enforce Microsoft Azure Multi-Factor Authentication (MFA) by using conditional access for all users who are NOT physically present in the office.
What should you include in the configuration?
- A. an Azure MFA Server
- B. a named location in Azure Active Directory (Azure AD)
- C. a sign-in risk policy
- D. a user risk policy
Answer: B
Explanation:
References:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/location-condition
NEW QUESTION 155
You have an Azure Active Directory (Azure AD) tenant named Contoso.com that contains the users shown in the following table.
The User Administrator role is configured in Azure AD Privileged Identity Management (PIM) as shown in the following exhibit.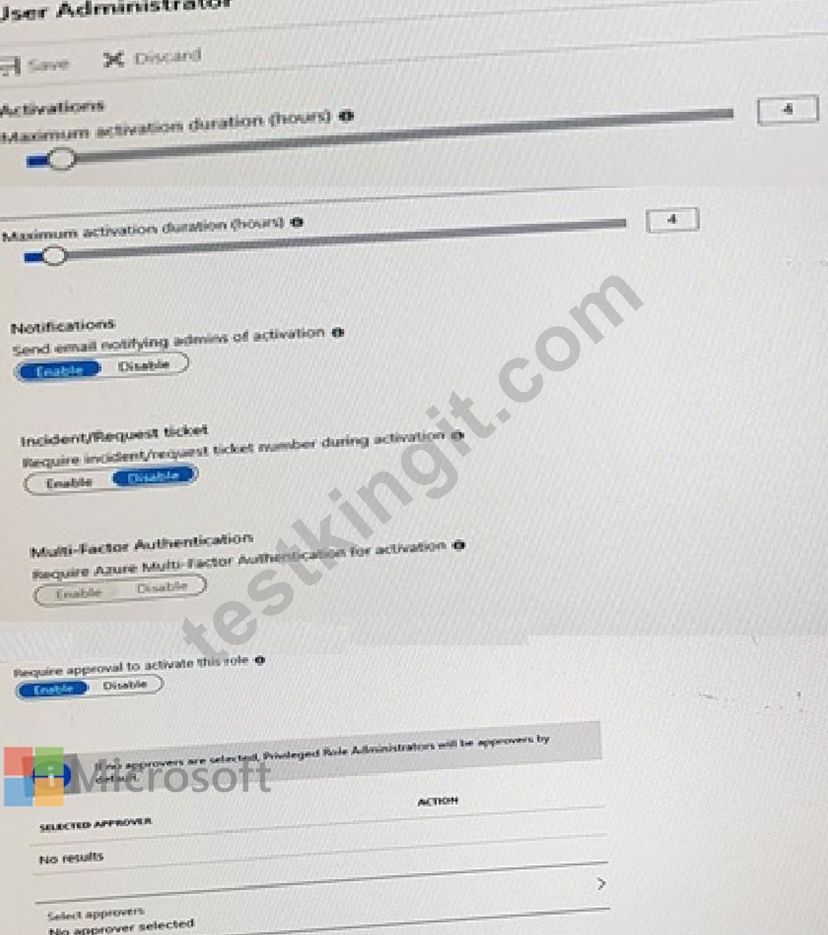
You make User4 eligible for the User Administrator role.
For each of the following statements, Select Yes if the Statement is true. Otherwise, select No./ NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 156
You have a Microsoft 365 E5 subscription.
All computers run Windows 10 and are onboarded to Windows Defender Advanced Threat Protection (Windows Defender ATP).
You create a Windows Defender machine group named MachineGroupl.
You need to enable delegation for the security settings of the computers in MachineGroupl.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation: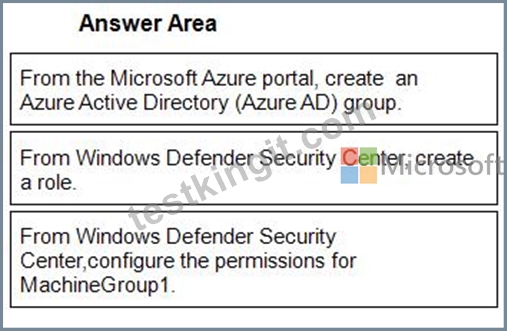
1 - From the Microsoft Azure portal, create an Azure Active Directory (Azure AD) group.
2 - From Windows Defender Security Center, create a role.
3 - From Windows Defender Security Center,configure the permissions for MachineGroup1.
NEW QUESTION 157
You have a Microsoft 365 subscription.
You have a site collection named SiteCollection1 that contains a site named Site2. Site2 contains a document library named Customers.
Customers contains a document named Litware.docx. You need to remove Litware.docx permanently.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
NEW QUESTION 158
次の図に示すように、管理者はAzure AD特権ID管理を構成します。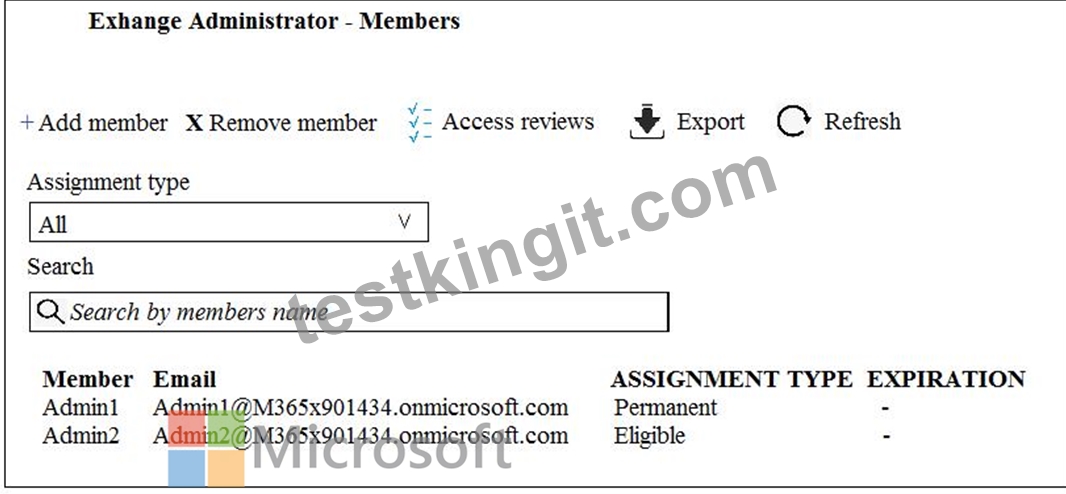
セキュリティ要件を満たすためにあなたは何をすべきですか?
- A. Admin1の割り当ての種類を[適格]に変更します。
- B. Azure Active Directory管理センターから、Exchange管理者の役割をAdmin2に割り当てます。
- C. Azure Active Directory管理センターから、Exchange管理者の役割をAdmin1に削除します。
- D. Admin2の割り当ての種類を固定に変更します。
Answer: A
Explanation:
テストレット1
概要
Fabrikam、Inc.は、パートナー小売店を通じて製品を販売する製造会社です。 Fabrikamは持っています
ヨーロッパ全域のオフィスに5,000人の従業員がいます。
既存の環境
ネットワークインフラ
ネットワークにはfabrikam.comという名前のActive Directoryフォレストが含まれています。 FabrikamはハイブリッドMicrosoftを持っています
Azure Active Directory(Azure AD)環境。
同社は特定のアプリケーション用にいくつかのオンプレミスサーバーを維持していますが、ほとんどのエンドユーザーは
アプリケーションは、Microsoft 365 E5サブスクリプションによって提供されます。
問題ステートメント
Fabrikamは以下の問題を指摘しています。
先週の金曜日以来、ITチームは "Unhealthy"を含む自動電子メールメッセージを受信しています。
件名の「Identity Synchronization Notification」を参照してください。
マルウェアを含む電子メールの添付ファイルを最近開いたユーザーが何人かありました。削除するプロセス
マルウェアは時間がかかりました。
必要条件
計画された変更
Fabrikamは以下の変更を実装する予定です。
Fabrikamは、Active Directoryへの疑わしいサインインを監視および調査する計画です。
Fabrikamは、パートナーにMicrosoft 365に保存されている一部のデータへのアクセスを提供する計画です。
アプリケーション管理
Fabrikamは、ワークロードアプリケーションを管理するための以下のアプリケーション要件を識別しています。
ユーザー管理者はさまざまな国から働きます
ユーザー管理者はAzure Active Directory管理センターを使用します
Admin1とAdmin2という2人の新しい管理者がMicrosoftの管理を担当します。
Exchange Onlineのみ
セキュリティ要件
Fabrikamは、以下のセキュリティ要件を確認しています。
ユーザー管理者によるAzure Active Directory管理センターへのアクセスは、毎回確認する必要があります。
七日間。管理者が3日以内にアクセス要求に応答しない場合、アクセス権は
削除されました
Microsoft 365のワークロードを管理するユーザーは、
一度に3時間まで。グローバル管理者はこの要件から除外する必要があります。
ユーザーが会社のデータを表示するために外部ユーザーを招待できないようにする必要があります。グローバル管理者のみ
User1というユーザーは招待状を送信できる必要があります
Azure Advanced Threat Protection(ATP)は、機密性を高めるためにセキュリティグループの変更をキャプチャする必要があります。
Active DirectoryのDomain Adminsなどのグループ
ワークロード管理者は、ワークロード管理者からサインインするときに多要素認証(MFA)を使用する必要があります。
匿名またはなじみのない場所
管理者がAzureに認証されるときにユーザー管理者の場所を監査する必要があります。
広告
マルウェアを含む添付ファイルを含む電子メールメッセージは、マルウェアなしで配信する必要があります。
愛着
可能な限り最小限の特権の原則を使用する必要があります
NEW QUESTION 159
You have the Microsoft conditions shown in the following table.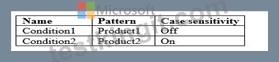
You have the Azure Information Protection labels shown in the following table.
You have the Azure Information Protection policies shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Answer:
Explanation:
Explanation
NEW QUESTION 160
You have a Microsoft 365 subscription.
You need to be notified by email whenever an administrator starts an eDiscovery search.
What should you do from the Security & Compliance admin center?
- A. From Search & investigation, create an eDiscovery case.
- B. From Alerts, create an alert policy.
- C. From Search & investigation, create a guided search.
- D. From Events, create an event.
Answer: B
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/alert-policies
NEW QUESTION 161
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: #HSP.ug?$p6un
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11122308


You need to ensure that a user named Allan Deyoung receives incident reports when email messages that contain data covered by the U.K. Data Protection Act are sent outside of your organization.
To complete this task, sign in to the Microsoft 365 admin center.
Answer:
Explanation:
See explanation below.
Explanation
1. In the Security & Compliance Center > left navigation > Data loss prevention > Policy > + Create a policy.
2. Choose the U.K. Data Protection Act template > Next.
3. Name the policy > Next.
4. Choose All locations in Office 365 > Next.
5. At the first Policy Settings step just accept the defaults,
6. After clicking Next, you'll be presented with an additional Policy Settings page Deselect the Show policy tips to users and send them an email notification option.
Select the Detect when content that's being shared contains option, and configure the number instances to be 10.
Select the Send incident reports in email
Select the Choose what to include in the report and who receives it link to add Allan Deyoung as a recipient.
7. > Next
8. Select the option to turn on the policy right away >
9. Click Create to finish creating the policy.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-test-tune-dlp-policy?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/compliance/data-loss-prevention-policies?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/compliance/what-the-dlp-policy-templates-include?view=o365-w
NEW QUESTION 162
Your company has a Microsoft 365 subscription, a Microsoft Azure subscription, and an Azure Active Directory (Azure AD) tenant named contoso.com.
The company has the offices shown in the following table.
The tenant contains the users shown in the following table.
You create the Microsoft Cloud App Security policy shown in the following exhibit.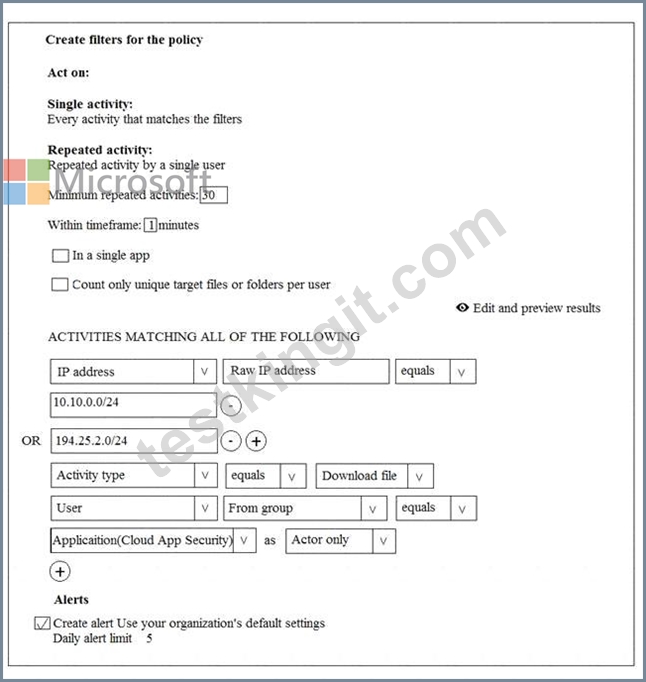
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.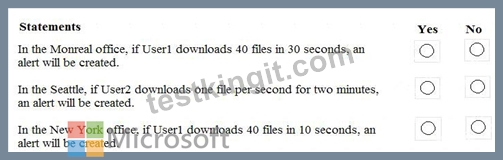
Answer:
Explanation:
Explanation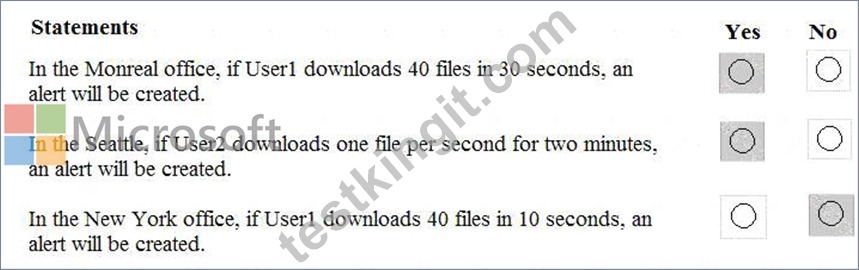
NEW QUESTION 163
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: #HSP.ug?$p6un
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11122308




You need to ensure that a user named Allan Deyoung can perform searches and place holds on mailboxes, SharePoint Online sites, and OneDrive for Business locations. The solution must use the principle of least privilege.
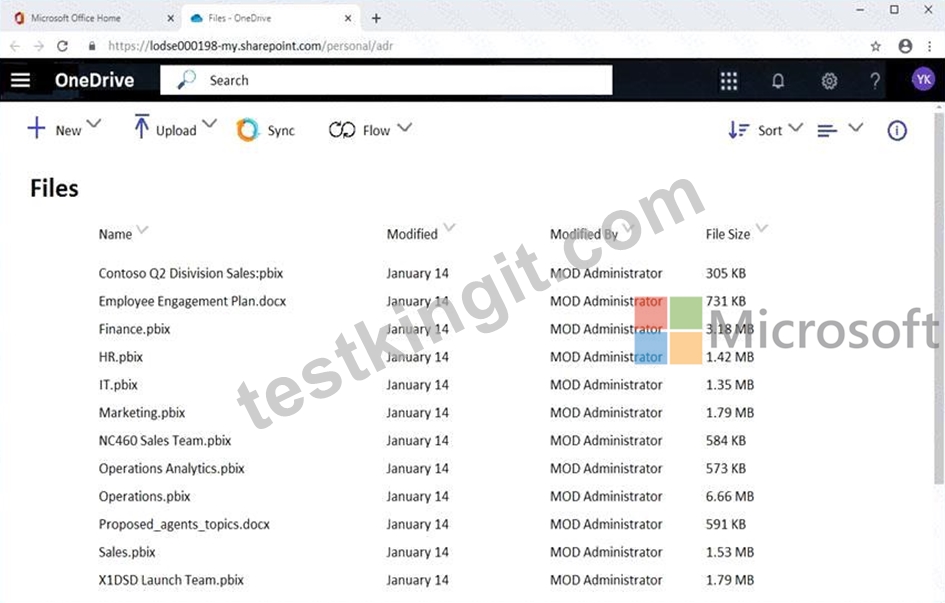
To complete this task, sign in to the Microsoft 365 admin center.
Answer:
Explanation:
See explanation below.
Explanation
* After signing in to the Microsoft 365 admin center, navigate to the Security & Compliance Center.
* In the left pane of the security and compliance center, select Permissions, and then select the checkbox next to eDiscovery Manager.
* On the eDiscovery Manager flyout page, do one of the following based on the eDiscovery permissions that you want to assign.
To make a user an eDiscovery Manager: Next to eDiscovery Manager, select Edit. In the Choose eDiscovery Manager section, select the Choose eDiscovery Manager hyperlink, and then select + Add.
Select the user (or users) you want to add as an eDiscovery manager, and then select Add. When you're finished adding users, select Done. Then, on the Editing Choose eDiscovery Manager flyout page, select Save to save the changes to the eDiscovery Manager membership.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/assign-ediscovery-permissions?view=o365-worldwi
NEW QUESTION 164
You have an Azure Acme Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.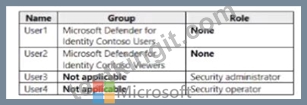
You discover several security alerts are visible from the Microsoft Defender for Identity portal.
You need to identify which users m contoso.com can dose the security Alerts. Which users should you identify?
- A. User3 and User4 only
- B. User1 and User3 only
- C. User1 and User2 only
- D. User1 only
- E. User4 only
Answer: A
NEW QUESTION 165
You have a Microsoft 365 subscription that include three users named User1, User2, and User3.
A file named File1.docx is stored in Microsoft OneDrive. An automated process updates File1.docx every minute.
You create an alert policy named Policy1 as shown in the following exhibit.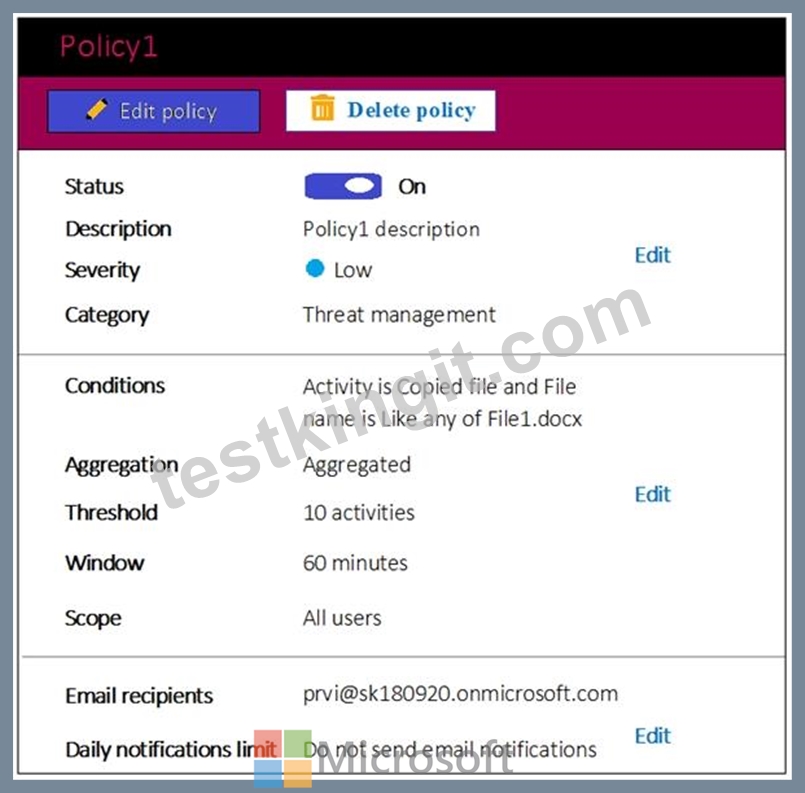
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: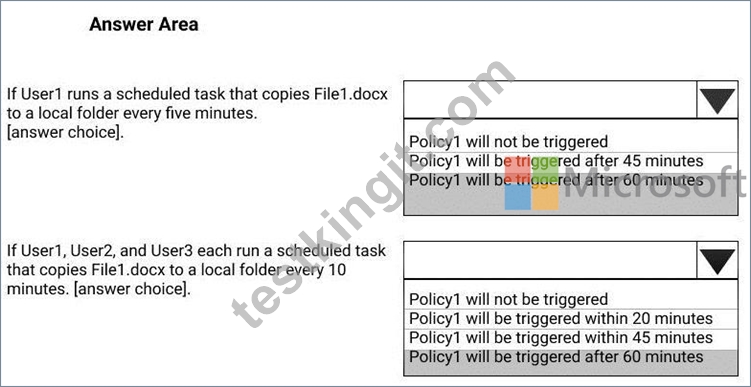
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/alert-policies
NEW QUESTION 166
You have a Microsoft 365 subscription.
You enable auditing for the subscription.
You plan to provide a user named Auditor with the ability to review audit logs.
You add Auditor to the Global administrator role group.
Several days later, you discover that Auditor disabled auditing.
You remove Auditor from the Global administrator role group and enable auditing.
You need to modify Auditor to meet the following requirements:
* Be prevented from disabling auditing
* Use the principle of least privilege
* Be able to review the audit log
To which role group should you add Auditor?
- A. Security reader
- B. Security operator
- C. Compliance administrator
- D. Security administrator
Answer: B
Explanation:
Explanation/Reference:
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/permissions-in-the-security-and-compliance- center
NEW QUESTION 167
You view Compliance Manager as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/meet-data-protection-and-regulatory-reqs-using-microsoft-cloud
NEW QUESTION 168
You have a Microsoft 365 E5 subscription.
From Microsoft Azure Active Directory (Azure AD), you create a security group named Group1. You add 10 users to Group1.
You need to apply app enforced restrictions to the members of Group1 when they connect to Microsoft Exchange Online from non-compliant devices, regardless of their location.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation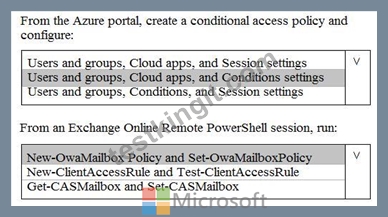
NEW QUESTION 169
......
Important Details to Know about MS-500 Exam
During MS-500 test, candidates will be required to undertake 40 to 60 questions within 180 minutes. The questions will be mostly provided in the form of multiple-choices in which the learner will choose the correct answer out of several options. Also, other types of inquiries may take place such as drag-and-drop, best answer, etc. In case there is a technical issue with the exam, one can post a challenge on the exam issue channel or contact customer care for technical problems.
Candidates can take the exam in Japanese or English language. To register for it, one should visit the Pearson VUE portal, create and account, choose “proctored exams”, and follow the instructions. Also, there is an enrollment fee required that is around $165 and is determined by the value of the currency of a particular country and the region. Taxes may be included conditionally based on the regional location. Notice that the fee is paid for each attempt. In case you fail the test in the first try, you may retake it after 24 hours. The next attempt is available in 14 days. One can sit for the same exam not more than five times in a year.
Latest 100% Passing Guarantee - Brilliant MS-500 Exam Questions PDF: https://selftestengine.testkingit.com/Microsoft/latest-MS-500-exam-dumps.html